Given that the start of the break out, governments and companies have actually rushed to develop apps and websites that can assist users identify COVID-19 signs.
India’s largest cell network Jio, a subsidiary of Reliance, launched its coronavirus self-test symptom checker in late March, right before the Indian federal government imposed a stringent across the country lockdown to avoid the more spread of the coronavirus. The symptom checker permits anyone to examine their symptoms from their phone or Jio’s website to see if they may have become infected with COVID-19
However a security lapse exposed among the symptom checker’s core databases to the internet without a password, TechCrunch has discovered.

Jio’s coronavirus sign checker. Among its databases exposed users’ reactions. (Image: TechCrunch)
Security scientist Anurag Sen found the database on May 1, just after it was very first exposed, and informed TechCrunch to inform the company.
” We have taken immediate action,” stated Jio representative Tushar Pania. “The logging server was for monitoring efficiency of our site, planned for the minimal purpose of people doing a self-check to see if they have any COVID-19 symptoms.”
The database consists of millions of logs and records starting April 17 through to the time that the database was pulled offline. The server included a running log of site mistakes and other system messages, it also consumed vast numbers of user-generated self-test data. Each self-test was logged in the database and included a record of who took the test– such as “self” or a relative, their age, and their gender.
The information also included the person’s user representative, a small bit of details about the user’s internet browser variation and the os, frequently utilized to fill the website effectively but can also be used to track a user’s online activity
The database likewise contains specific records of those who signed up to produce a profile, allowing users to update their symptoms over time. These records included the responses to each concern asked by the sign checker, including what symptoms they are experiencing, who they have been in contact with, and what health conditions they may have.
Some of the records likewise included the user’s accurate place, however only if the user enabled the symptom checker access to their browser or phone’s place data.
We have actually published a redacted part of one of the records below.
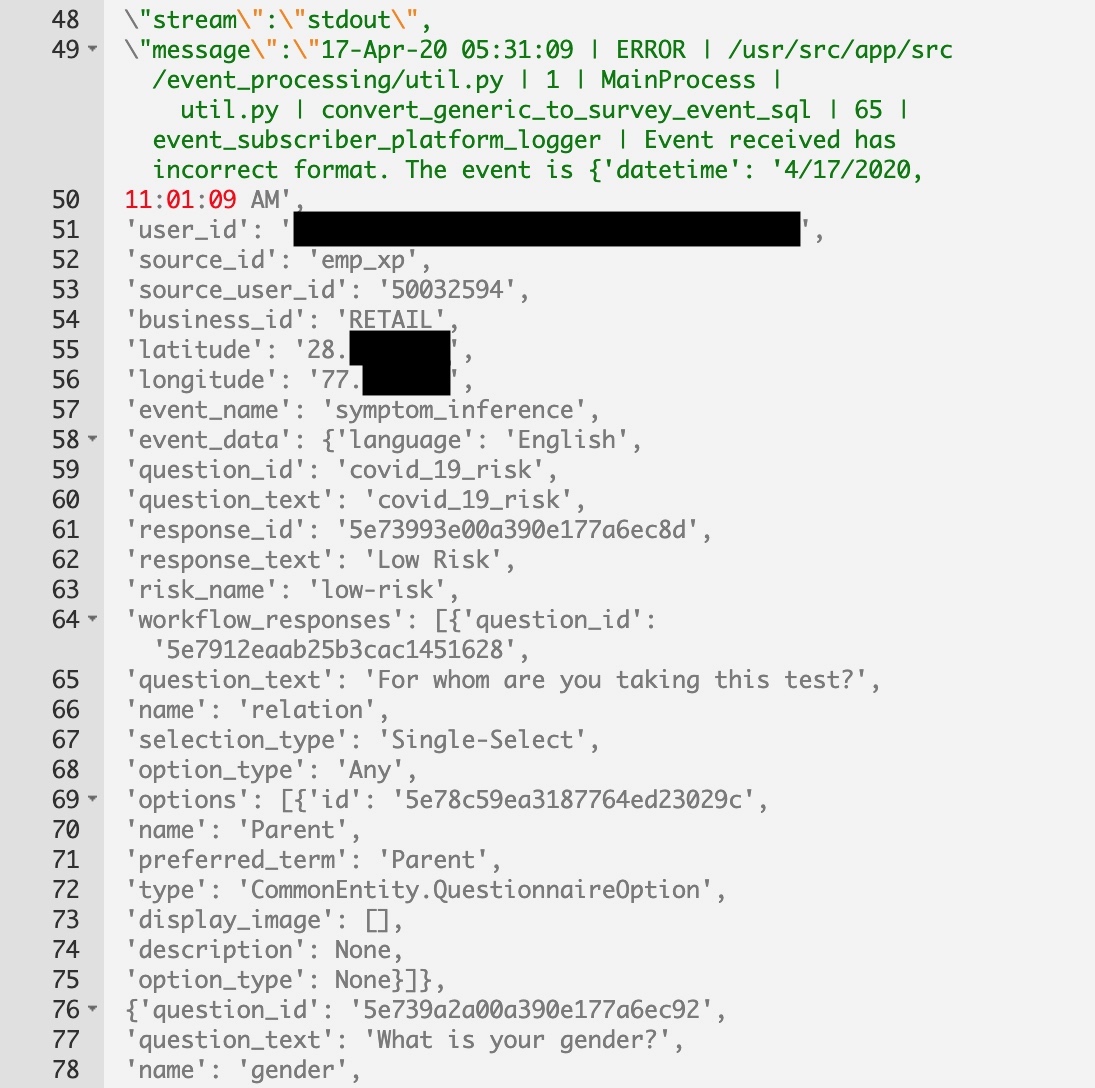
A redacted portion of the exposed database. (Image: TechCrunch)
From one sample of data we acquired, we found countless users’ accurate geolocation from across India. TechCrunch was able to determine individuals’s homes utilizing the latitude and longitude records found in the database.
Most of the location data is clustered around significant cities, like Mumbai and Pune. TechCrunch also discovered users in the UK and North America.
The exposure could not come at a more crucial time for the Indian telecoms giant. Recently Facebook invested $ 5.7 billion for a near-10%stake in Jio’s Platforms, valuing the Reliance subsidiary at about $66 billion.
Jio did not address our follow-up questions, and the company did not say if it will inform those who used the symptom tracker of the security lapse.
Comments
Post a Comment